Recent Updates RSS
The latest changes across PCI SSC resources and EMVCo specifications.
Yes. Assessors have two options when performing PCI DSS testing procedures; they can either: 1) test a representative sample of the population according to the assessor's defined sampling methodology, or …
Payment terminals (sometimes referred to as point-of-sales systems, point-of-interaction devices, or payment devices) are physical devices that capture payment card data to process transactions. Because these devices are directly involved …
Encryption of cardholder data with strong cryptography is an acceptable method of rendering the data unreadable according to PCI DSS Requirement 3.5.1. However, encryption alone is insufficient to render the …
Where a third-party service provider (TPSP) receives and/or stores only data encrypted by another entity, and where they do not have the ability to decrypt the data, the TPSP may …
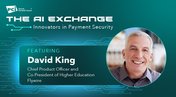
Welcome to the PCI Security Standards Council’s blog series, The AI Exchange: Innovators in Payment Security. This special, ongoing feature of our PCI Perspectives blog offers a resource for payment …
via finsidersbrasil.com.br
PCI SSC changed the URL format for these FAQs. Content is unchanged.
Oct. 14, 2026 · Edinburgh, Scotland
Aug. 25, 2026 · Johannesburg, South Africa
June 17, 2026 · Mumbai, India
April 23, 2026 – April 24, 2026 · Okinawa, Japan